The Domain Name System is one of the Internet’s essential services. It translates familiar domain names into the IP addresses that computers use to communicate. That convenience also creates an important security question: how can a resolver know that the DNS answer it received is authentic and has not been replaced in transit?
DNS Security Extensions, usually called DNSSEC, address that problem with digital signatures. DNSSEC allows a validating resolver to verify where DNS data came from and whether it changed after the authoritative zone signed it. It strengthens trust in DNS without replacing the DNS protocol or encrypting ordinary DNS queries.
What problem does DNSSEC solve?
Traditional DNS was designed for availability and speed, not for cryptographic verification. A resolver can ask an authoritative server for a record, but the basic protocol does not prove that the response is genuine. An attacker who succeeds in inserting a forged answer could direct visitors to an unintended server even when they typed the correct domain name.
This risk is easier to understand after reviewing how the Domain Name System resolves a name. DNSSEC adds verifiable signatures to that process. A validating resolver can reject a forged or altered response instead of treating it as legitimate DNS data.
How DNSSEC creates a chain of trust
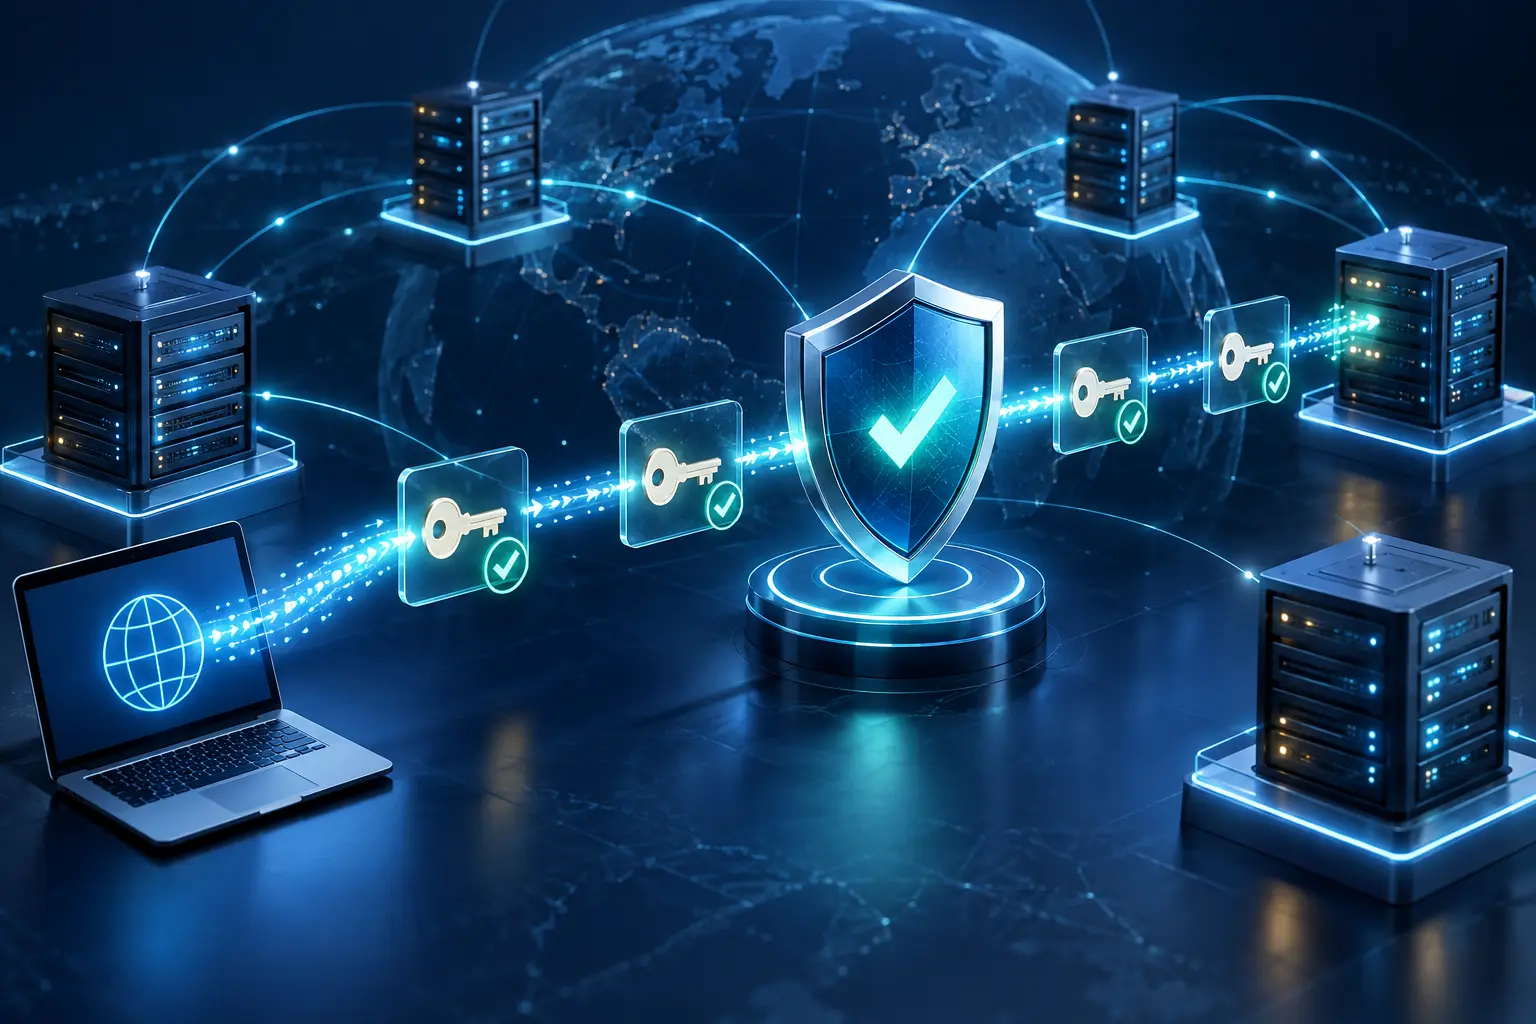
DNSSEC does not rely on one universal key for every domain. It creates a chain of trust that begins at the DNS root and continues through the top-level domain to the signed domain. Each level can securely point to the key used by the level below it.
DNSKEY records publish public keys
A signed zone publishes its public keys in DNSKEY records. The corresponding private keys remain protected by the zone operator and are used to sign groups of DNS records. Keeping the private key secure is critical because anyone who obtains it may be able to produce signatures that appear valid.
RRSIG records contain digital signatures
For each signed record set, the authoritative zone supplies an RRSIG record. A validating resolver uses the appropriate DNSKEY to check that signature. Successful validation confirms both the origin of the data and its integrity: the response was signed by the expected zone and was not modified after signing.
DS records connect parent and child zones
A DS record in the parent zone contains a digest associated with a key in the child zone. For example, a registrar can publish a domain’s DS information in the relevant top-level-domain zone. The resolver follows these references from a previously trusted level, building a verifiable path to the final answer.
NSEC and NSEC3 authenticate negative answers
DNSSEC must also prove when a requested name or record does not exist. NSEC and NSEC3 records provide authenticated denial of existence. This prevents an attacker from simply returning an unsigned “not found” response for valid signed data.
What DNSSEC protects—and what it does not
DNSSEC provides DNS data origin authentication, integrity protection, and authenticated denial of existence. These controls help defend against forged DNS answers and cache-poisoning scenarios when validation is performed correctly.
However, DNSSEC does not encrypt DNS traffic. Anyone able to observe an unencrypted DNS query may still see the requested name. DNSSEC also does not secure a vulnerable website, repair an infected server, prevent every distributed denial-of-service attack, or protect a registrar account with a weak password. HTTPS, access controls, monitoring, backups, and secure account practices remain necessary.
Why deployment has two important sides
DNSSEC works only when zone signing and validation connect correctly.
- Authoritative side: The domain owner or DNS provider signs the zone, publishes DNSKEY and signature records, and keeps the signatures current.
- Parent-side delegation: The correct DS record is published through the registrar or registry so the parent can establish trust in the child zone.
- Resolver side: A validating recursive resolver checks the signatures and the chain of trust before returning an answer to the client.
If a signed zone changes its keys without updating the parent DS information correctly, validating users may receive failures even though the records look normal to a non-validating resolver. Careful key rollover and monitoring are therefore part of operating DNSSEC, not optional housekeeping.
A practical DNSSEC deployment checklist
- Confirm support. Check that the authoritative DNS provider, registrar, and top-level domain all support the required DNSSEC workflow.
- Review current DNS data. Make sure the zone is accurate before signing it. DNSSEC can authenticate incorrect data just as effectively as correct data.
- Enable zone signing. Generate or activate the signing keys through the authoritative DNS service and confirm that DNSKEY and RRSIG records appear.
- Publish the DS record. Submit the exact DS values through the registrar. A mismatch can break validation for the domain.
- Test from validating resolvers. Confirm the complete chain of trust, not merely the presence of DNSSEC records.
- Monitor signatures and rollovers. Watch expiration dates, DS consistency, and planned key changes. Include DNSSEC checks in routine DNS monitoring.
Reliable authoritative infrastructure still matters after a zone is signed. Features such as redundant servers, anycast distribution, monitoring, and failover address availability rather than authenticity. The distinction is similar to the operational benefits discussed in the guide to Premium DNS: security and resilience are strongest when several complementary controls work together.
DNSSEC is a trust layer, not a complete security stack
A successful DNSSEC deployment gives validating resolvers cryptographic evidence that DNS data is authentic. It reduces an important class of DNS manipulation risk, but it should be combined with HTTPS, secure registrar access, multi-factor authentication, protected signing keys, monitored DNS changes, and resilient authoritative service.
For a practical overview of the technology, see DNSSEC, the DNS Security extension. The protocol’s security model and requirements are defined in RFC 4033: DNS Security Introduction and Requirements.