Every visit to a website usually begins with a DNS lookup. Your device asks a resolver to translate a domain name into an IP address, then uses that address to contact the destination. Traditional DNS queries are commonly sent without encryption, which means someone able to observe the network may see the names being requested or interfere with the exchange.
DNS over HTTPS, abbreviated DoH, carries DNS queries and responses inside an encrypted HTTPS connection. It can improve privacy and protect DNS traffic while it travels between a client and a compatible resolver. However, it is not a complete anonymity tool, and a good deployment depends on choosing a trustworthy resolver and understanding how DoH interacts with browser, device, and network policies.
How DNS over HTTPS works
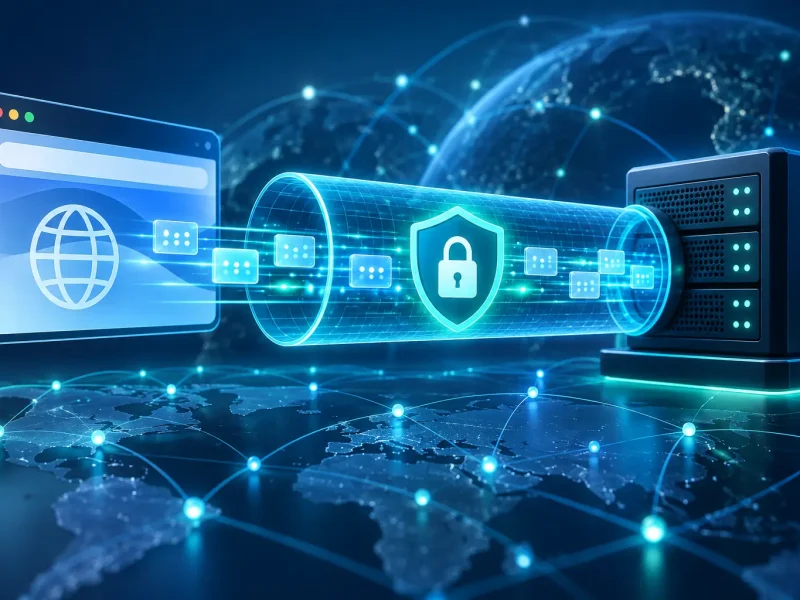
The underlying DNS question remains familiar: the client still asks for records such as A, AAAA, or MX. The difference is the transport. Instead of sending the request as ordinary DNS traffic, the client encodes it in an HTTPS request to a DoH endpoint. TLS encrypts that connection and authenticates the server certificate, while HTTP provides the request-and-response layer.
If you want to review the lookup process first, this introduction to how the Domain Name System works explains the path from a domain name to an address. DoH changes the protected connection between the client and recursive resolver; it does not replace authoritative DNS or alter the records published by a domain owner.
DoH compared with traditional DNS and DoT
Traditional DNS normally uses UDP or TCP on port 53. DNS over TLS, or DoT, encrypts DNS through a dedicated TLS connection, conventionally on port 853. DoH uses HTTPS, usually on port 443, so its traffic travels through the same protocol family used by websites and web APIs. For a direct comparison of the two encrypted transports, see this guide to DoT and DoH.
Neither transport is automatically better in every environment. DoT is straightforward for network administrators to identify and manage. DoH can work well inside browsers and applications and may be more resilient on networks that restrict dedicated DNS ports. The right choice depends on whether DNS policy is controlled centrally, per device, per application, or by the user.
The privacy and security benefits
Protection against local observation
Encryption prevents a passive observer on the path between the client and DoH resolver from reading the DNS request directly. This is valuable on public Wi-Fi and other untrusted local networks, where plaintext DNS could otherwise expose browsing-related metadata. The observer can still see IP addresses and other traffic characteristics, but the DNS message itself is protected inside TLS.
Integrity while the query is in transit
TLS also makes it substantially harder for an on-path party to modify the DNS exchange between the client and resolver. The client authenticates the DoH service through its HTTPS certificate and rejects traffic that fails the connection’s integrity checks. This protects the transport channel, provided the client configuration and certificate validation are correct.
Consistent resolver behavior across networks
An application configured with a specific DoH resolver may use the same service as a device moves between home, office, and mobile networks. That consistency can avoid unexpected resolver changes. It can also create policy conflicts, however, if an application bypasses a resolver that an organization relies on for internal names, filtering, incident response, or compliance.
What DoH does not protect
DoH encrypts one segment: communication from the client to the selected recursive resolver. The resolver must process the query and may be able to associate it with network metadata. Privacy therefore shifts from the local network or access provider toward the resolver operator. Before selecting a service, review its logging, retention, jurisdiction, filtering, and security policies rather than assuming that encryption alone guarantees privacy.
DoH also does not hide all browsing activity. A network observer may infer destinations from IP connections, traffic patterns, and other metadata. DoH is not a substitute for HTTPS on the website, a VPN, secure endpoint configuration, or careful browser privacy settings.
It is equally important to distinguish encrypted DNS transport from DNS data authentication. DoH protects the channel to the resolver, while DNSSEC lets a validating resolver verify signed DNS data. The two technologies solve different problems and can be used together. The article DNSSEC Explained describes that chain-of-trust model in more detail.
Browser-level and system-level deployment
DoH in a browser
A browser can send its own lookups to a DoH provider. This is convenient and can improve privacy for browser activity, but other applications on the same device may continue using the operating system’s DNS configuration. Troubleshooting becomes harder if the browser and system receive different answers or apply different filtering policies.
DoH at the operating-system or network layer
System-level configuration can provide a consistent encrypted resolver for multiple applications. Managed organizations may instead deploy an approved resolver through device policy or a controlled gateway. Administrators should test internal domain resolution, split-horizon DNS, parental controls, threat blocking, captive portals, and incident logging before a broad rollout.
How to choose a DoH resolver
A resolver becomes an important trust point, so selection should be based on more than latency. Evaluate:
- Privacy policy: Determine which query and client data is logged, why it is collected, and how long it is retained.
- Security practices: Look for current TLS support, DNSSEC validation, abuse response, and transparent operational documentation.
- Reliability: Consider geographic reach, redundancy, historical uptime, and how the client behaves if the service is unavailable.
- Filtering behavior: Decide whether you need an unfiltered response, malware protection, family filtering, or organizational policy controls.
- Performance: Test real lookup latency from the networks and regions your users actually use rather than relying on a global average.
DNS availability still matters because failed resolution makes healthy websites appear offline. Resilient authoritative DNS, monitoring, and failover complement encrypted client-to-resolver transport. This overview of Premium DNS capabilities explains several availability-oriented considerations on the authoritative side.
A practical deployment checklist
- Define the goal. State whether the priority is privacy on untrusted networks, consistent policy, malware filtering, or another measurable outcome.
- Select and document the resolver. Review its privacy and security policies, endpoints, availability, and support model.
- Choose the control layer. Decide whether DoH belongs in the browser, operating system, managed endpoint, or network gateway.
- Test normal and internal names. Confirm public websites, private zones, VPN resources, captive portals, and local services resolve as expected.
- Plan failure behavior. Know whether the client fails closed, falls back to plaintext DNS, or switches to another encrypted resolver.
- Monitor after rollout. Measure lookup latency, resolution errors, policy impact, support cases, and resolver reachability.
The protocol details, including the HTTPS request formats and media types used for DNS messages, are defined in RFC 8484: DNS Queries over HTTPS.
Conclusion
DNS over HTTPS can prevent local networks and on-path observers from directly reading or modifying DNS messages between a client and resolver. Its value is real but specific: it protects DNS transport, not every layer of a browsing session. A sound deployment combines an appropriate control layer, a carefully evaluated resolver, clear fallback behavior, compatibility testing, and complementary protections such as HTTPS and DNSSEC.